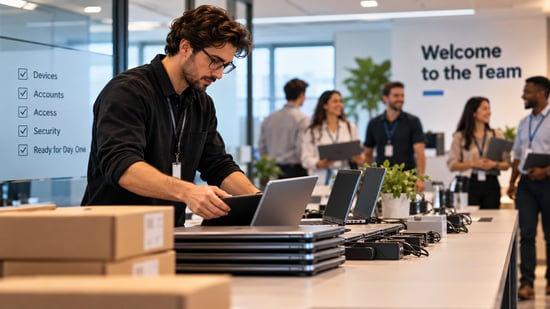
 Hiring twenty employees a month can look manageable on a recruitment plan. For IT, the same growth means a continuing stream of laptops to prepare, accounts to create, permissions to approve and first-day problems to resolve. When those tasks arrive as individual last-minute requests, even a capable support team can develop a backlog that delays productivity.
The solution is not simply to ask IT to work faster. Growing businesses need a repeatable onboarding process that connects hiring forecasts, device supply, identity management, security and employee support. The goal is straightforward: every new starter should have a secure, usable working environment when their role requires it, without making routine setup depend on an administrator remembering every step.
Why Rapid Hiring Exposes IT Bottlenecks
Twenty hires in a month do not necessarily arrive evenly. Several may start on the same Monday, work remotely, require specialist applications or join a newly opened location. A standard laptop may be available while the required software licence, approval for financial systems or network access is still missing. The backlog is often a coordination problem rather than a shortage of technical skill.
That distinction matters when leaders decide how to respond. More support staff can relieve pressure, but adding people without improving handoffs may simply increase the number of tickets moving through an inconsistent process. Fundz has examined how growing companies outrun their IT support capacity as headcount, software and locations expand. New-hire preparation is one of the clearest places to see that pressure.
Successful onboarding should be measured by the employee's ability to perform essential tasks, not merely by whether a laptop has been delivered or an IT ticket has been closed. A device with no working authentication, missing applications or the wrong permissions is not ready for use.
Start with the Hiring Forecast and a Clear Definition of Ready
HR, hiring managers and IT need one agreed source of information for upcoming starters. At minimum, a confirmed request should contain the employee's start date, location, manager, role, working arrangement, required device type and any approved specialist software. The process should also distinguish a forecast vacancy from a confirmed appointment so that equipment can be planned without creating unnecessary accounts or licences.
Define what ready for day one actually means. For most office roles, that might include a delivered and managed device, a working identity, multifactor authentication, approved core applications, connectivity and a clear support contact. Role-specific access should be separately approved; it should not be guessed from a job title alone.
A simple operating sequence can clarify responsibilities:
| Stage | Owner | Required Outcome |
|---|---|---|
| Hiring forecast | HR and department leaders | Expected volumes, locations, and likely start dates are visible to IT. |
| Confirmed hire | HR and hiring manager | Identity details, role profile, and exceptional access requirements are approved. |
| Pre-start preparation | IT or service partner | Device, baseline applications, and account setup are prepared and checked. |
| First-day validation | New hire and IT support | Sign-in, essential applications, and the route to help are tested. |
| Early follow-up | Hiring manager and IT | Missing access and recurring issues are resolved and recorded. |
Set lead times around actual supplier delivery, approval and configuration requirements. A single universal target is less useful than a realistic commitment for each role and location. An exceptional late hire should enter a visible priority path instead of quietly displacing every planned setup.
Standardise Devices and Access Before Automating Them
Automation works best when the underlying process is consistent. Establish a small number of supported device configurations and role-based application packages. A sales starter might need a CRM, calling tools and collaboration software; a finance starter may need accounting applications and more tightly controlled data access. Both can share the same security baseline without receiving identical permissions.
Document which requirements are standard and which require an exception. Standard requests can move quickly; exceptions should have named approvers, a business justification and a record of what was granted. This prevents the common shortcut of copying a colleague's entire access profile, which may include rights the new employee does not need.
Device management platforms can apply policies and install approved applications during setup. Microsoft's Windows Autopilot documentation, for example, describes preparing and configuring corporate Windows devices using cloud-based management. It does not remove the need for supported hardware, enrolment prerequisites, dependable connectivity or application testing. Organisations should pilot device profiles before deploying them at scale.
Maintain an accurate inventory of equipment, licences and spare devices. A modest pool of tested replacements can help absorb unpredictable arrivals, but inventory levels should reflect procurement lead times and actual hiring patterns, not an arbitrary stock target.
Connect HR Records to Identity and Access Management
Creating accounts manually from email requests increases the risk of errors, duplicate identities and inconsistent permissions. Where the systems support it, an approved HR record can trigger the creation or preparation of an employee identity, while role and manager information guide subsequent access requests. Microsoft describes HR-driven provisioning as a way to connect workforce records with identity creation and lifecycle changes.
That integration must be designed carefully. A start date changing in HR should update the provisioning schedule; a cancelled hire should not retain active credentials; and a person transferring roles should have unnecessary access removed as well as new access added. Multifactor authentication, least-privilege permissions and appropriate logging belong in the standard workflow.
Separate account preparation from access activation. IT may need to configure systems ahead of a start date, but that does not mean a future employee should automatically gain access to sensitive business information before authorised employment begins. Account activation and high-risk entitlements should follow documented policy and approval rules.
Use External IT Capacity Where It Removes a Real Constraint
Businesses do not always need to build permanent internal capacity for every hiring spike. A managed or co-managed IT provider may be able to stage equipment, coordinate shipping, prepare devices, handle routine help-desk requests or provide on-site assistance at additional locations. Internal leaders should still retain control of security policies, application ownership, purchasing decisions and the definition of a completed onboarding.
For organisations operating in Texas, suppliers offering technology management in San Antonio may be worth considering for regional support. Location alone is not evidence of faster deployment, however. The right questions concern device stock, delivery coverage, the availability of technicians, remote setup capability and what happens when several employees start together. The guide to whether a business service provider really needs to be local explains why physical proximity should be judged against the work that actually requires it.
Similarly, businesses considering whether to deploy IT with InterDev should assess the provider's proposed onboarding responsibilities, escalation arrangements and coverage against their own hiring requirements. The provider publishes managed and co-managed IT services, but a claimed reduction from a two-week setup to three days cannot be treated as a verified customer outcome without supporting evidence.
Put the expected results into a service agreement or operating plan: when a completed request must be received, who supplies equipment, who approves access, how exceptions are escalated and what counts as ready. An SLA promising to acknowledge a ticket quickly is not the same as a commitment to deliver a usable workstation.
The Cost of Delays Is Wider Than the IT Queue
When a new employee cannot access essential tools, the cost extends beyond the support ticket. A manager may spend time chasing updates, colleagues may lend equipment or repeat explanations, and the employee may lose the opportunity to complete planned training or customer-facing work. Such delays can affect the employee's first impression, although a specific retention or productivity impact should not be assumed without evidence.
To make the problem visible, record the hours between the employee's scheduled start and the point when essential work becomes possible. Track recurring reasons for delay, such as late HR notification, unavailable devices, missing licences, incomplete manager approval or configuration failures.
Where the business wants to estimate financial impact, combine documented waiting time with an appropriate internal cost assumption and clearly label the result as an estimate, not a proven loss of revenue.
This is more useful than repeating broad industry percentages that may measure general employee onboarding rather than IT setup. The business can then decide whether improving forecast accuracy, changing a supplier arrangement or automating a particular task would produce the greatest benefit.
Make the First Week Part of the IT Process
Provisioning is not complete simply because the first login works. New employees need to know where to report missing access, how to enrol authentication methods, which devices are approved for work and how to reach support if they are remote. A brief first-day checklist or onboarding portal can provide those instructions without creating another disconnected information store.
Give hiring managers a clear role in validation. They should confirm that the employee can perform the tasks required for their position and identify specialist application gaps that IT may not recognise. A short follow-up during the first week can reveal problems that only emerge after initial training.
Keep broader employee induction separate but connected. HR and managers remain responsible for training, role expectations and team integration; IT is responsible for a secure, working technology environment. Treating these as complementary processes avoids suggesting that better laptop deployment alone will solve employee retention.
Build Capacity Around Measurable Onboarding Performance
Once the basic process is established, review a small set of indicators each month: the share of starters ready at the required time, median provisioning time, late or incomplete requests, first-week IT incidents and the leading causes of exceptions. Break results down by department, location and device profile where volumes allow. A company-wide average can hide an unreliable process for remote staff or specialist teams.
Use those findings to adjust capacity. Repeated device delivery delays point towards inventory or fulfilment changes; application access delays may indicate unclear ownership or licence shortages; excessive manual rework suggests that role profiles and automation rules need attention. The right investment follows the constraint rather than the most visible technology product.
Onboarding twenty employees every month without a growing setup backlog is therefore a matter of operating discipline. Accurate forecasts, approved role profiles, secure identity workflows, dependable device supply, clear ownership and first-week support make hiring growth easier to absorb. Automation and external service providers can strengthen that model, but neither compensates for a process that starts too late or lacks a definition of success.
When Hiring Gets Complicated: Questions IT Leaders Should Plan For
What should happen when a new employee is confirmed only two days before their start date?
Use an exception process rather than bypassing security controls. Check whether a tested spare device and a preapproved baseline application package can cover essential work. Escalate missing manager approvals and record any temporary limitations. Tell the employee and their manager what will be ready, what will follow later and who owns each outstanding item. Repeat emergencies should be reviewed with HR rather than becoming the normal workflow.
Should contractors and temporary workers use the same onboarding process as permanent employees?
They can use the same request and identity-tracking system, but their access profiles should reflect their work and expected end dates. Require a responsible internal sponsor, grant only necessary permissions, and schedule reviews or expiry of accounts and licences. Check contractual and data-access requirements before giving external workers the same tools or records as employees.
Can someone use a personal laptop if a company device has not arrived?
Only where an approved bring-your-own-device policy and technical controls permit it. Consider what data the person will access, whether the device can meet authentication and protection requirements, and whether a managed virtual workspace is available. Where those conditions are not met, provide a controlled loan device or adjust the initial work plan instead of improvising access to sensitive systems.
How can IT prepare accounts in advance without allowing access too early?
Stage the identity and configuration separately from account activation. Use approved start-date rules, authentication requirements and entitlement approvals before enabling access. Test what happens when a start date is postponed, or an offer is withdrawn, including downstream SaaS accounts that may not automatically inherit the central identity system's status.
What if an employee changes departments shortly after joining?
Treat the change as a new authorised access event, not simply an extra set of permissions. The new manager should approve what is required, the former manager or system owner should identify rights to withdraw, and IT should confirm that licences and shared resources match the updated role. This avoids access accumulating whenever employees move within the organisation.