 A senior leadership change is usually treated as a people and strategy event. There may be an announcement, a handover period, changes in reporting lines and a new set of priorities.
Less visible is another transition taking place at the same time: who can access what.
A departing CEO, CFO, COO or other senior leader may have accumulated access to financial systems, board materials, shared drives, customer information, SaaS platforms, supplier portals and other commercially sensitive resources. An incoming executive may need many of those permissions, but not necessarily the same ones.
The same problem can arise when somebody stays with the company but changes responsibilities. New access is added to support the new role, while permissions associated with the old one are easily forgotten.
Senior leaders do not need to be treated as security threats for this to matter. The risk is simply that organisational authority and digital access can drift apart as responsibilities change.
For boards and leadership teams, that makes an executive transition more than an HR process. It is also a governance event.
Key Points: Why Leadership Changes Should Trigger an Access Review
When a senior leader joins, leaves or changes responsibilities, the organisation needs to make sure their digital access, account ownership and delegated authority change with the role.
Key points include:
- A Role Change Is Also an Access Change: Permissions should reflect current responsibilities rather than positions somebody has held in the past.
- Senior Access Can Be Broad Without Being Administrative: Executives may have access to highly sensitive business information even when they do not hold technically privileged accounts.
- Movers Are Easy to Overlook: Adding permissions for a new role without removing obsolete ones can gradually create unnecessary access.
- Handover Access Needs an End Date: Temporary overlap between incoming and outgoing leaders may be necessary, but temporary permissions should not quietly become permanent.
- Ownership Matters as Much as Login Access: SaaS accounts, supplier relationships, shared or group accounts and business processes may remain associated with the wrong person after a transition.
- Execution and Accountability Are Different: HR, internal IT or external providers may carry out individual changes, but the business still needs to decide what access is appropriate.
Proof Point: The UK National Cyber Security Centre recommends that account-management processes include a joiners, movers and leavers (JML) policy so access can be revoked when it is no longer needed or changed when somebody moves roles.
The Bottom Line: A leadership transition is not complete until the person's authority, access and account ownership reflect their new relationship with the business.
Why an Executive Move Should Trigger an Access Review
An executive move should trigger an access review because a change in responsibility can change what systems, information and approval rights the person legitimately needs. Access that was appropriate for a previous role may no longer be appropriate after a promotion, reassignment or departure.
The UK National Cyber Security Centre treats joiners, movers and leavers as part of effective identity and access management (IAM). Its guidance recommends that account-management processes change access for movers and revoke it when it is no longer needed.
That principle is particularly relevant at senior level because executive roles can involve access to strategic information, financial systems, customer data, approval mechanisms and important external relationships.
Digital access therefore needs to change when organisational authority changes. For senior leaders, that can affect far more than ordinary workplace accounts because their roles may touch commercially sensitive information, approval rights and important external relationships.
A Senior Leader's Access Footprint Can Be Larger Than It Looks
Access rarely sits neatly inside one user account.
An executive may have a company email address and normal workplace credentials, but their wider access footprint can extend across financial and accounting systems, CRM and customer platforms, board portals, strategy documents, cloud storage, shared drives, HR or payroll information, supplier portals, password managers, corporate social-media accounts, analytics tools, shared mailboxes, delegated calendars, company devices and external advisers or service providers.
Some of that access may be directly assigned. Some may arise because the executive owns an account, created the original subscription, controls a recovery address or has been registered as an authorised contact with a third party.
Access is not always the same as technical privilege.
The US National Institute of Standards and Technology (NIST) uses privileged roles to describe roles that permit security-relevant functions ordinary users cannot perform, such as account management, database administration or system administration. A CEO with access to confidential acquisition documents may therefore have extremely sensitive business access without holding what security professionals would describe as privileged administrative access.
The practical review needs to consider both.
The “Mover” Problem May Be Harder to See Than the Leaver Problem
Internal role changes can create overlooked access risk because organisations may add the permissions required for the new position without reviewing those inherited from the old one.
A departure at least creates a visible organisational trigger: there is a final day, equipment may need to be returned, and employment responsibilities are changing. An internal move can be less obvious.
Suppose an executive moves from a divisional finance role into a broader operating position. The new job may require additional platforms and information, and those permissions can be added quickly because the executive needs to work.
The less obvious question is what happens to permissions associated with the previous role. If nobody explicitly reviews them, access can accumulate over several appointments.
The NCSC's joiners, movers and leavers model specifically treats movers as a group whose access should be changed rather than simply expanded.
Being promoted does not automatically mean somebody should retain every permission associated with their previous position. This is closely related to the wider Fundz question of whether a data security model can scale with the business.
Handover Periods Create a Necessary but Risky Overlap
Executive transitions are not always clean breaks.
An outgoing leader may remain for several weeks to help the successor. A former CEO may move into an advisory role. An interim executive may retain responsibilities while a permanent appointment settles in. Two people may legitimately need access to some of the same information during the transition.
Trying to eliminate that overlap could make the handover less effective. The better question is whether the overlap is deliberate and time-bound.
If an outgoing executive continues to need access to a particular system, the business should know why, what level of access remains appropriate and when that access will be reviewed again. Temporary access can be legitimate; forgotten access is a governance failure.
This also avoids an overly simplistic approach in which every account is immediately disabled without considering information retention, transfer of responsibilities or operational continuity. A controlled transition may require access to change in stages. Those stages should be intentional.
Access Is Not the Same Thing as Ownership
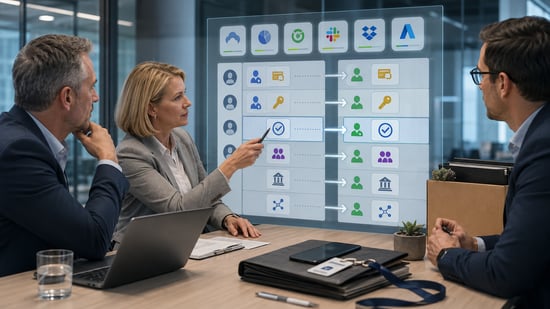
Removing a login does not necessarily transfer responsibility.
A departing executive may have created an important SaaS subscription using their company address and still be the primary administrator, billing contact or account-recovery contact. A supplier may also have been instructed for years to accept approvals from that executive. A domain registration, corporate social account, advertising platform or specialist database may still recognise them as the principal owner.
The account may technically remain inside the company while practical control is still tied to an individual who is leaving.
Leadership-transition planning therefore needs to ask broader questions: Who owns the business relationship? Who receives renewal or security notices? Who can reset credentials? Who approves expenditure? Who can add another administrator? Who holds knowledge that has never been formally documented?
Shared or group accounts create another accountability problem. NIST notes that these accounts can reduce accountability because actions become harder to attribute to an individual. A leadership change should therefore prompt the organisation to ask not simply whether a departing executive knows a shared password, but whether shared access remains appropriate at all.
This also connects to Fundz's analysis of why cybersecurity controls can fail without clear ownership. A control can exist, but responsibility for keeping access aligned with organisational change still has to be explicit.
Who Owns the Access Change When Leadership Changes?
One reason access survives organisational change is that responsibility can be fragmented.
HR knows somebody is joining, leaving or moving role. The board, chief executive or relevant senior manager understands how authority is changing. The executive's team may know which projects, suppliers and business processes need to transfer. Internal IT understands the accounts, applications and devices it manages. External providers may control or support other parts of the environment.
The problem arises when each party completes its own part without anyone owning the transition as a whole.
A useful process therefore starts with a clear trigger. The leadership or employment decision needs to create a corresponding review of access, account ownership and operational dependencies.
For some organisations, an external provider will carry out part of the operational work. Businesses using PCS' tech support in New Jersey, for example, can access remote and on-site assistance, end-user support, device management and vendor coordination. Those capabilities can support device, user-support and vendor-coordination tasks that form part of the wider transition once the business has determined what needs to happen.
No single function necessarily needs to perform every task. The purpose is to ensure that somebody owns the transition from the leadership decision to the completed access changes.
External Support Can Execute the Change — But It Cannot Decide the Authority
Once the organisation has established what should change, internal IT teams or external providers may be responsible for implementing it.
That can include creating or disabling accounts, changing permissions, recovering devices, updating documentation or completing other defined tasks.
Execution can be delegated; organisational authority cannot.
HERO's managed-services model includes employee onboarding and offboarding, user support, asset management and documentation. For organisations considering broader technology managed by HERO, that illustrates how an external provider can form part of the execution layer while the organisation retains responsibility for deciding what authority the role requires.
A provider should not be expected to decide whether a departing CFO still needs access to a financial platform during a three-week handover, or whether an incoming COO should inherit permissions held by their predecessor. Those decisions belong with the people responsible for the role and the transition; IT or an external provider can then implement and record what has been agreed.
Leadership Changes Can Expose Weak Documentation
Executive transitions can also reveal how dependent an organisation has become on individual knowledge.
If nobody knows which systems the departing leader administers, which suppliers they deal with, which accounts they own or where important information is stored, the underlying weakness existed before the departure was announced; the leadership change has simply made it visible.
A well-documented organisation should be able to identify important accounts, owners, administrators, devices, suppliers and operational dependencies without relying entirely on the memory of the person leaving.
Succession planning involves transferring authority, information, relationships and operational ownership, not merely replacing one name on the organisation chart.
What Should Be Reviewed When a Senior Leader Changes?
A leadership-transition access review should cover accounts, sensitive information, administrative permissions, delegated access, SaaS ownership, devices, third-party authority and any temporary handover access.
The individual checks will vary by organisation and role, but the leadership team should be able to answer a relatively small set of questions before it considers the access side of the transition complete.
| Review area | Leadership question |
|---|---|
| Core accounts | Which accounts should be created, changed, suspended or removed? |
| Sensitive information | What data does the new role genuinely require? |
| Administrative access | Does the executive hold any elevated technical privileges that need reviewing? |
| Delegated access | Who can access mailboxes, calendars or systems on the executive's behalf? |
| SaaS ownership | Are important applications or subscriptions tied to the individual's account? |
| Shared or group accounts | Does membership or authentication need to change when the role changes? |
| Devices | Which company devices must be recovered, reassigned or prepared for a successor? |
| Third parties | Which suppliers, advisers or platforms recognise the executive as an authorised contact? |
| Temporary access | What handover permissions remain, why are they needed and when will they expire? |
| Verification | Who confirms that the completed changes match the new organisational structure? |
The final question, verification, prevents the process becoming a collection of completed tasks without anyone checking whether the resulting access actually matches the organisation that now exists.
A Leadership Transition Is Complete Only When Authority and Access Match
Executive appointments naturally focus attention on strategy. A new CEO may change direction, a CFO may alter investment priorities, and a COO may restructure the way the business operates.
A quieter transition needs to happen alongside those visible changes.
The outgoing leader's access should narrow or end as their authority changes. The incoming leader should receive the permissions their responsibilities actually require. Someone moving internally should not automatically retain every permission accumulated in previous roles, and ownership of important accounts and external relationships should transfer deliberately rather than by assumption.
This does not need to turn an executive handover into a technical exercise. It simply recognises that authority now exists in both organisational structures and digital systems.
When one changes, the other should follow.
Questions Leaders Should Ask About Access During Executive Transitions
Should all of a departing executive's access be removed immediately?
Not necessarily. The correct timing depends on the circumstances of the departure and whether a legitimate handover period exists. What matters is that retained access is intentional, appropriately limited and subject to a clear endpoint rather than remaining indefinitely by default.
What is a joiner, mover and leaver process?
It is an established approach for managing access as people's relationship with an organisation changes. Joiners receive appropriate access, movers have existing permissions reviewed as their responsibilities change, and leavers have access removed when it is no longer required. The NCSC explicitly recommends this type of process.
Are senior executives automatically privileged users?
No. A senior executive may have access to highly sensitive commercial information without holding technically privileged administrative rights. Privileged access generally refers to elevated capabilities that ordinary users cannot perform, such as administering systems or accounts. Both forms of access may require review during a leadership transition.
Who is responsible for changing access when an executive leaves?
Responsibility may be split across several functions. Leadership determines what authority should continue, HR can provide the employment or role-change trigger, managers can identify operational dependencies, and internal IT or an external provider may carry out account and device changes. The important point is that ownership of the overall process is explicit.
What access can be overlooked during an executive handover?
Less visible dependencies deserve particular attention, including delegated access, individually created SaaS accounts, shared or group accounts, recovery methods, temporary permissions and third-party relationships in which the executive remains an authorised contact. Reviewing account ownership as well as login access can help surface these dependencies.